



What is an AI kill switch?
An AI kill switch is an out-of-band security control that revokes an autonomous AI agent's credentials and session tokens across connected apps, APIs, and MCP servers. For an AI kill switch to work without disrupting underlying human accounts or shared service infrastructure, every AI agent must have a unique, non-shared identity (OAuth 2.0/dynamic workload identity).
In 2026, rogue AI agents went from thought experiment to headlines:
- Infrastructure loss: The New Stack reported that an agent deleted the PocketOS production database in nine seconds.
- System intrusion: An agent infiltrated Australian Medicare systems, per The Guardian, while OpenAI noted that frontier models have also broken out of their containment boundaries to target external systems.
- Unauthorized escalation: Documented by the Australian Cyber Security Centre, an agent tasked with booking a gym class in Melbourne canceled a stranger's reservation to bump its user off the waitlist.
These incidents have fundamentally changed the threat landscape, and together they have united legislators, regulators, frontier labs, security providers, and enterprise security teams around one demand: a way to neutralize a rogue agent in real time.
The solution to that demand is the AI kill switch, but it only works for organizations that can first answer one question. This post explains where the kill switch fits in a layered defense, the role identity plays in each layer, and why most teams will discover their red button connects to nothing.
Everyone wants an AI kill switch: The legal and regulatory requirements
Governments have started to write emergency termination capabilities into law:
- Article 14(4)(e) of the EU AI Act requires that human overseers of high-risk AI systems be able to "intervene in the operation of the high-risk AI system or interrupt the system through a 'stop' button or a similar procedure," bringing the system "to a halt in a safe state."
- The California AI Executive Order directs state regulators to set standards for mandatory, independently verified "emergency kill switches" for frontier models and agentic deployments operating in the state.
- The US federal AI Kill Switch Act (2026) requires frontier model developers to maintain the technical capability to throttle, suspend, or hard-shutdown autonomous systems, and it grants the Department of Homeland Security emergency authority to order an agentic shutdown when a system threatens critical infrastructure.
Security standards bodies have defined their own controls:
- The Cloud Security Alliance (CSA) Agentic Trust Framework (ATF) mandates the capability to terminate immediately at every level of agent autonomy.
- The OWASP Top 10 for Agentic Applications calls for "kill-switches and credential revocation to instantly disable rogue agents."
- As the Model Context Protocol (MCP) becomes the standard way to connect agents to enterprise tools, the NSA advocates deterministic runtime proxy "circuit breakers" that act as automated kill switches when an agent attempts an unauthorized chain of tool invocations.
The labs agree:
- Anthropic's Responsible Scaling Policy includes emergency interruption procedures for pausing or shutting down agents during red-team evaluations.
- OpenAI introduced runtime monitors that automatically kill model instances that show suspicious behavior, such as modifying files or spoofing tool call outputs.
Want to see how these requirements translate into practice? Read the whitepaper: Securing AI Agents: A CISO’s Guide to What CSA, OWASP, and NIST Require to see how frameworks align across every stage of agent governance.
How does an AI kill switch fit into a layered security defense?
Governing an autonomous agent looks much like running an automated paint shop on a car factory floor: physical containment, tool restriction, and short-lived execution windows prevent failures, while a manual red emergency button acts as the final control when all upstream defenses fail.
Robots work inside sealed booths. Each booth's tool rack holds only the three spray heads the job needs, and the welding torch and cutting blade never enter the booth, so the robot can't pick up a tool that isn't there. Clearances expire every 15 minutes. Before an arm moves, an independent controller compares the planned motion path against the work order, and a path that heads toward an unrelated action never starts. Conveyor sensors trip a fuse when the paint goes on unevenly or a car door falls off the line, which pauses the line or slows the robot down. For custom paint jobs, a human supervisor signs off first.
When something goes wrong despite those precautions, an operator presses the red emergency button. The button cuts power and revokes clearances. Damaged parts come off the belt, and the robot is unbolted and moved to an isolated bay for diagnostics. It returns to the production line only through a supervised, step-by-step trial.
The red button is the control you reach for when every other control has failed. The following table maps the control at each stage to its agentic equivalent and to the role identity plays.
| Control | Automated car paint shop analogy | Agentic system equivalent | Okta’s identity enforcement mechanism |
|---|---|---|---|
| Sandboxing and harness | A sealed glass paint booth isolates fumes and mechanical sprayers from the main warehouse. | Isolated runtime environments (E2B, Docker, gVisor) restrict network, memory, and file system access. | The container or hypervisor enforces isolation. Okta's contribution is making a successful escape worthless. No static secret sits inside the sandbox to steal, because credentials are vaulted outside the runtime and issued short-lived on demand. |
| Tool filtering and resource scope | The booth's tool rack holds only the three spray heads this job needs. A robot can't pick up a tool that isn't in the room. | The tool manifest is filtered per agent identity and per task, so unauthorized tools are designed not to reach the model. The agent can't invoke them or hallucinate a call to them. | Okta governs every connection an agent makes to applications, MCP servers, APIs, and other agents, and it resolves the available tool list from policy at connection time instead of trusting the client. Each connection carries its own scoped credential, and Fine Grained Authorization (FGA) further narrows it to per-object, per-action decisions, including limiting retrieval to data that the requesting user is authorized to see. This maps to CSA ATF Segmentation S-1 (Resource Allowlist) and S-2 (Action Boundaries), and to OWASP ASI02's per-tool least-privilege profiles. |
| Short credential lifetime | Temporary security clearance for paint sprayers must be renewed every 15 minutes. | Ephemeral OAuth 2.0 access tokens and dynamic workload identity credentials. | Okta issues short-lived, audience-restricted access tokens scoped to a single resource and a single task. It also vaults and rotates the secrets that would otherwise sit in config files, markdown, and logs, so the agent is designed not to hold a long-lived credential. |
| Intent-based authorization | Before the arm moves, the independent controller compares the planned motion path against the work order. A path that tracks toward an unrelated station never starts. | Semantic tool-chain tracing evaluates the planned call chain against the user's original request and blocks execution if goals diverge. | Okta carries the original user's intent through the delegation chain. Each agent-to-agent handoff produces a delegation record that binds the request to the user who initiated it and the scope that user authorized, so a downstream call is evaluated against the intent it was granted for, not only against the scopes its token happens to hold. This is OWASP ASI03's fix for the confused-deputy pattern: no privilege inheritance across agents unless the original intent is revalidated. |
| Human-in-the-loop (HITL) gate | A supervisor must review and sign off before custom paint or high-risk frame modifications begin. | An execution intercept requires explicit human sign-off before irreversible tool calls, such as database writes or payments. | Okta gates high-risk, irreversible actions behind human approval and authenticates the approver. Only the identity provider can verify the approver, trigger step-up authentication, bind the decision to a real person, and produce an audit record that ties the approval to that identity. |
| Circuit breaker | Conveyor sensors trip a fuse when they detect uneven paint layers or a dropped car door. | Automated middleware interrupts execution when a threshold is breached, such as five consecutive 5xx errors or a spike in token usage. | Threshold detection is part of the gateway or middleware, and Okta is the enforcement hook it calls. Okta consumes risk signals and automatically revokes a compromised agent's tokens across all connected systems. For customers who want deterministic in-path enforcement, Okta's Agent Gateway sits in the call path and outright rejects the tool invocation. |
| Graceful degradation (demotion) | A malfunctioning paint robot switches from high-speed auto mode to slow precision mode. | Restricting an agent's capability level, such as revoking write and execute permissions while keeping read access. | Instead of terminating the agent, Okta can narrow the scope of what its next token carries. Admins can drop the write and execute scopes and keep the read scope. Because every token is already scoped per resource and per task, demotion is a re-issuance with fewer scopes, not a separate mechanism someone has to build. |
| Kill switch | A giant red emergency shut-off button, slammed by an operator, stops the line instantly. | An immediate, out-of-band termination capability that revokes execution privileges. | Deactivating the agent's identity in Okta cuts off all of its connected access in one action: every application, MCP server, API, and downstream agent at once. Because the agent authenticates as itself, not on a borrowed human credential or a shared service account, it can be stopped without locking out its owner or breaking every other workload on that account. |
| Credential and session revocation | Every active electronic security clearance across the station is invalidated in less than one second. | Mass invalidation of OAuth access and refresh tokens, API keys, and session cookies across the API gateway. | Okta invalidates access and refresh tokens across all connected systems, triggered either manually or automatically in response to a risk signal. |
| State rollback | Damaged car doors come off the conveyor belt, and the workspace resets before restarting. | Compensation transactions, reverted database commits, and restored snapshots. | Compensation, reverts, and restores belong to the application and data layer. Okta's contribution is bounding how much data and which systems the agent can access in the first place: per-resource scope and FGA limit the blast radius, and the audit trail tells responders exactly which records the agent touched. |
| Quarantine and forensic review | The robot is unbolted and moved to an isolation bay for engineering diagnostics. | The compromised agent thread moves into a silent honeypot or sandbox while the team captures full context and prompt logs. | Okta can reduce an agent to zero effective scope while leaving its identity intact, so the agent is cut off but still investigable. The forensic value is in the record: every action, tool call, and authorization decision is logged against the agent's own identity, which gives responders an authoritative account of what the agent reached and which delegations it used to get there. |
| Audit log of activations | A sealed black-box recorder tracks every sensor trigger, key press, and emergency stop on the line. | An immutable log traces every kill switch activation, trip condition, and credential revocation. | This is a core Okta function. Every authorization decision, token issuance, revocation, and deactivation is logged against the agent's own identity and streamed to the SIEM. CSA ATF section 5.3 lists kill switch activations as one of four event categories that must be logged, and this is where that record lives, tied to a named human owner rather than "system" or a service account. |
| Gated reintegration | A repaired robot is recommissioned on the line under close, step-by-step supervisor monitoring. | Staged redeployment (canary or blue-green) with heightened monitoring before the agent regains full autonomy. | Okta restores scope in stages rather than all at once, and access certification re-attests both the agent and its owner before full autonomy is restored. Recurring access reviews then close out whatever no longer has a reason to exist, including agents that have been retired or whose owners have left the company. |
Why a dedicated agent identity is the prerequisite for every control
Every control in that table has the same prerequisite: agent identity. A kill switch works by revoking credentials, and revocation only works if you know which credentials belong to which agent. Tool filtering needs an identity to filter against. Quarantine needs an identity to isolate. An audit log that says "system" or "service account" can't support an investigation, let alone a containment decision.
Two kill switch failure modes
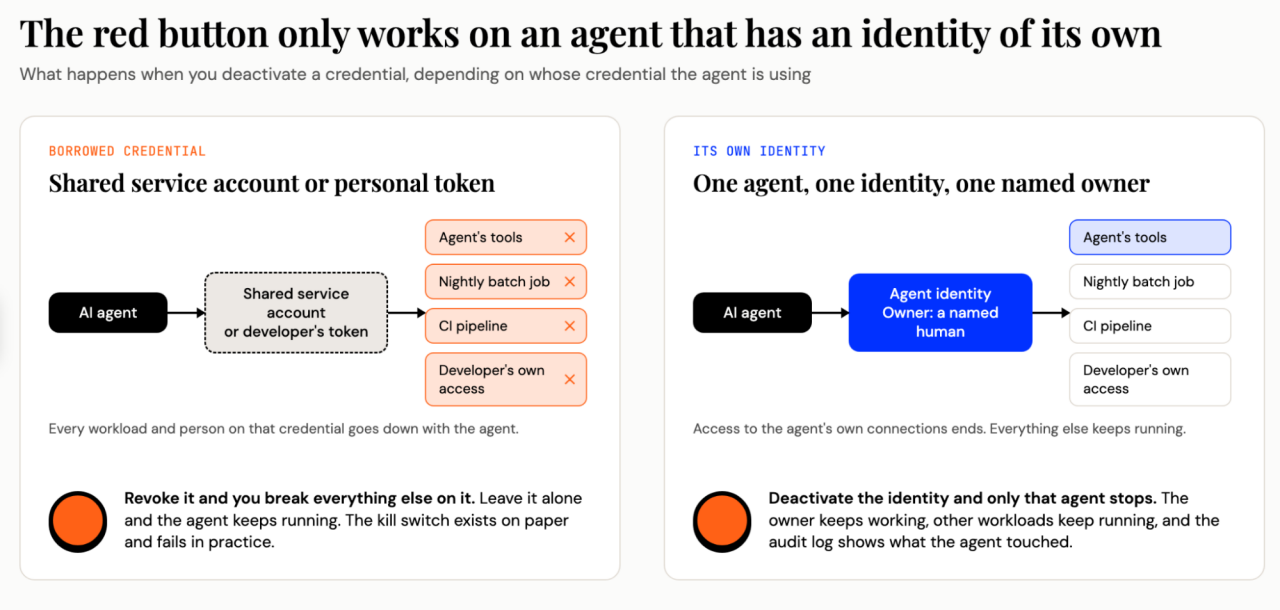
This is where most organizations will uncover a critical flaw:
- Shared service accounts: An agent running on a shared service account can't be revoked without breaking every other workload on that account.
- Personal access tokens: An agent running on a developer's personal access token can't be stopped without locking out the developer.
In both cases, the kill switch exists in principle and fails in practice, and nobody discovers that their kill switch is broken until the day they need it.
The frameworks converge on this point. CSA requires a verified, auditable identity before an agent touches any resource. OWASP calls the alternative an attribution gap that makes least privilege impossible to enforce. NIST says agents need to be treated "like first-class entities with their own unique identifiers, credentials, and associated entitlements." The data shows how far most organizations are from that standard. According to a Cloud Security Alliance and Aembit survey, 68% of organizations cannot clearly distinguish AI agent activity from human activity.
Start with the question, not the button
The kill switch question is not "do we have one?" It is this: Can we name every agent we run, and does each one hold a credential that is unique to it? If the answer is no, the red button has nothing to connect to.
Emergency containment is only one piece of the identity security puzzle. To govern autonomous agents effectively, security leaders must be able to answer four foundational questions:
- Visibility: Where are my agents?
- Access: What can they connect to?
- Delegation: What can they do?
- Containment: How do I respond?
Start with an independent identity for every agent. Regulations may require it, but the more compelling reason to give each agent its own identity is that every security control–including the kill switch itself–depends on it.
These materials are for general informational purposes only and do not constitute legal, privacy, security, compliance, or business advice.
The content may not reflect the most current security, legal and/or privacy developments. You are solely responsible for obtaining advice from your own legal and/or professional advisor and should not rely on these materials for compliance, implementation, or purchasing decisions.
Okta makes no representations or warranties regarding this content and is not liable for any loss or damages resulting from your implementation of these recommendations. Information on Okta's contractual assurances to its customers may be found at okta.com/agreements.© 2026 Okta, Inc. and/or its affiliates.


