The race is on. New AI tools are hitting the market weekly with promises of solving your exact challenge. And every company wants to implement AI—and fast.
As the person who sits at the intersection of Okta's technology, data, and AI intelligence, I feel that pressure. It’s a tough spot for IT, which can easily become the "Department of No." But I've learned that rushing to use this technology without a solid foundation leads to fragmented systems, security risks, and spiraling costs. It’s no different from the challenges we’ve faced in IT for years.
Given those high stakes, my industry peers and customers will often ask how we’re rolling out AI internally. We started by becoming customer zero and deploying our own products.
Being customer zero means we get to be the toughest critics of our own technology. We’re testing these capabilities at enterprise scale and communicating friction points directly back to our engineering teams, so the final product our customers get is battle-tested, securely designed, and built for real-world complexity.
Like so many companies, we're still on this journey, but here’s an honest reflection on where we are today, the lessons we’ve uncovered, and the steps that are keeping our rollout secure.
Lesson 1: Avoid death by a thousand agents
When AI tools first started showing up at Okta, adoption happened organically and teams found point solutions to solve specific problems. But it became clear pretty quickly that building or buying a custom AI agent for every use case wasn't going to scale.
Employees don't work in just one system, so their AI agents shouldn't either. If we'd kept building isolated agents for every workflow across our roughly 1,500 software applications, we'd have ended up with tens of thousands of them—or what I call death by a thousand agents.
So instead of fragmenting further, we made a bet that fewer, more capable agents would be more powerful than a sea of disparate ones. That’s why we built Okta One, a secure digital coworker platform and the orchestration layer for AI agents built at Okta.
We anchored our AI strategy around core personas, starting with employees and customers.
For employees, we built Dex, our first digital coworker on the Okta One platform. Dex is an orchestrating agent for IT, people, travel, and expense support that cuts across systems to remove friction for all employees. Take a new hire: in their first week, they have questions about benefits, they need access to specific systems, they need to connect their device to the network, they may have VPN questions. Historically, an employee had to already know which systems existed just to know where to ask the question. Dex removes that burden by giving them one front door.
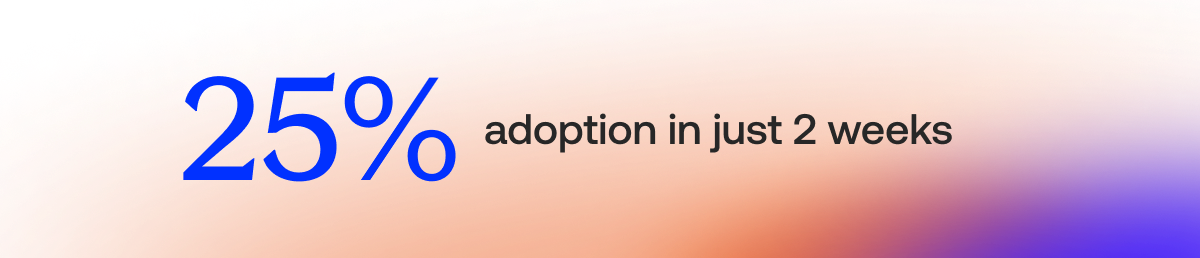
The early results have been encouraging: We reached 25% employee adoption in just two weeks, and that number has been climbing steadily since. To date, Dex has fielded over 23,500 interactions.
Lesson 2: Secure digital workers like human workers
So how do we govern an agent that has access to multiple disparate systems? We treat AI identity the same way we treat human identity. We want our AI agents—and the humans using them—to have access to exactly what they should, and nothing more.
In practice, that means every one of our agents, including super agents like Dex, is registered in Okta Universal Directory (UD), the same way a human identity would be. An agent shouldn’t have more access to systems and data than the human it’s acting on behalf of. Every time a user logs in to interact with an agent, that access is checked. We also rely on Secure Token Storage to manage how agents authenticate safely as they move across our ecosystem, rather than relying on static credentials. Building Dex with this architecture was possible because my team got early access to Okta for AI Agents. By treating agents as first-class identities, we always know where our agents are, what they can access, and what they can do—the foundational questions behind the blueprint for the secure agentic enterprise.
Crucially, this identity framework must extend beyond our own walls. We still use AI agents that live natively inside other tools, like Salesforce or Atlassian, but we need identity and governance to work consistently across them all. Even when an agent is native to a third-party platform, we tie its identity back to our central control plane using Okta, ensuring its access permissions are strictly governed and fully auditable. That's consistent with a philosophy we've held at Okta for a long time: we want to stay vendor-agnostic and interoperable so our customers aren’t locked into one provider, and I apply that same thinking to our AI architecture.
Lesson 3: Build boundaries before you build bots
Unleashing AI into your enterprise and hoping for the best isn’t a sound strategy. To deploy digital workers safely and sustainably, organizations must build strict boundaries around an agent's inputs, behaviors, and access. We know that without proactive governance and continuous oversight, enterprise AI can quickly become inaccurate, unpredictable, and incredibly expensive. Here’s where you need to draw the line:
Agents are only as good as their inputs
It takes real, sustained work to get your knowledge bases into a state where an agent can reliably give the right answer. AI can be confidently incorrect. That might be an acceptable tradeoff for a consumer app, but in the enterprise, it's a disaster. For instance, you can’t have a compensation agent that's only 80% accurate. Employees need to know they'll get paid the right amount, on time.
The cost of compute can spiral out of control
Tokens are expensive. Every time an agent's model call is made, it doesn't just process the task at hand—it also has to reason through the full menu of tools it could use, even the ones it never touches. Left unchecked, this "tool tax" can become one of the largest line items in an AI budget.
Our own approach has been to scope which tools an agent can see at the point it connects to a system, rather than exposing the entire tool catalog and hoping governance catches misuse after the fact. If an identity (human or agent) is only entitled to a handful of tools, that's the only set that should ever reach the model's prompt. Fewer tools visible to the model means fewer tokens spent, and it has the added benefit of shrinking the blast radius if something ever goes wrong.
Where we go from here
What we’ve built at Okta will continue to evolve. We're expanding Dex's capabilities to handle even more complex orchestrations—like letting an employee update a home address in Workday without ever logging into the HR platform directly—and we're rolling out specialized sub-agents for specific domains, like a Legal bot and a Procurement bot.
But this is what I want you to walk away with: You don’t need to have everything figured out before you get started. While our journey brought a lot of hard lessons, we relied on the bedrock of good IT—strong identity, strict access controls, and a commitment to security—to safely guide what we built, when we built it, and what systems we exposed.
If you're the one being asked to turn on AI for your company, resist the urge to buy every shiny point solution. What you really need is a foundation: identity and access sorted out first, a bias toward fewer and more capable agents, and a willingness to treat the inevitable hiccups as information rather than failure.
Come see us at Oktane, where we’ll pull back the curtain and show you how you can deploy secure AI agents when identity is your foundation.